Infra Lab
This project is designed as a hands-on learning experience to set up an on-premise Kubernetes cluster using KVM. It covers the deployment of core Kubernetes services and demonstrates how to automate infrastructure setup and application delivery using Infrastructure as Code (IaC) and GitOps principles, leveraging tools like OpenTofu and Flux.
Every step of the process—from planning and designing the cluster architecture to manually configuring each component—has been carefully documented. These guides are available in the documentation section, making it easy for anyone to replicate and build their own home Kubernetes cluster.
Directory Hierarchy
.
├── addons
│   ├── bind9
│   └── keycloak
├── docs
│   ├── assets
│   ├── getting-started
│   ├── playbooks
│   └── stylesheets
├── jarvis-kvm
│   ├── ansible        # Ceph playbooks (obsolete)
│   └── terraform
├── k0s
│   └── k0sctl.yaml
├── LICENSE
├── README.md
├── requirements.txt
└── zensical.toml
.git-crypt: contains gpg files of collaborators who can open encrypted git-crypt file.
jarvis-kvm: terraform code to provision VMs and other resources on top KVM hypervisor.
Technology Stack
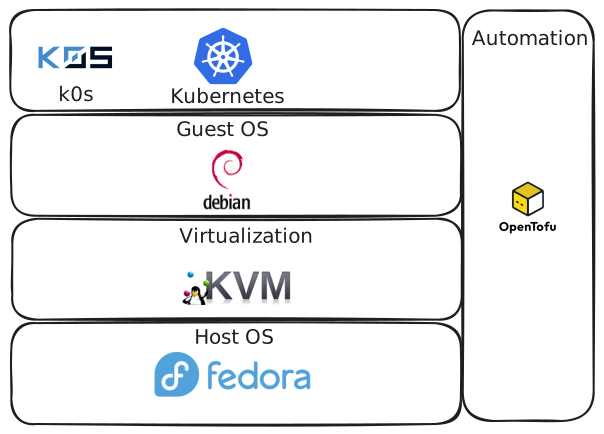
The following picture shows the high level components of opensource solutions used so far in the cluster, which installation process has been documented and its deployment has been automated with OpenTofu:
| Name | Description | |
|---|---|---|
 |
Flux | GitOps tool (manifests in gitops-fluxcd) |
 |
Cloud-init | Automate OS initial installation |
 |
Containerd | Container runtime integrated with K0S |
 |
Calico | Kubernetes Networking (CNI) |
 |
CoreDNS | Kubernetes DNS |
 |
Debian | VM OS (cluster nodes and general01) |
| Fedora | KVM host OS | |
 |
ExternalDNS | External DNS synchronization |
 |
Cert-manager | TLS Certificates management |
 |
K0S | The simple, solid & certified Kubernetes distribution that works on any infrastructure |
 |
KVM | Full virtualization solution for Linux on x86 hardware containing virtualization extensions (Intel VT or AMD-V) |
 |
MetalLB | Load-balancer implementation for bare metal Kubernetes clusters |
| BIND9 | Authoritative and recursive DNS for the lab zone, with TSIG dynamic updates | |
| Keycloak | Identity provider (OIDC, Dynamic Client Registration) for MCP servers | |
| agentgateway | Gateway API implementation for MCP and AI traffic | |
| External Secrets | Syncs secrets from external stores into Kubernetes | |
| Sealed Secrets | Encrypted secrets that are safe to store in Git | |
| Infisical | Secret store behind External Secrets (lab project, environment dev) |